all-projects2026
PROJECT_002 · Threat intelligence · Full-stack platform
ThreatCast PK crowdsourced threat intelligence
Pakistan's cyber threat command center: the community reports attacks, an Isolation Forest model flags coordinated campaigns for moderators, and verified events stream to a live map, analytics and real-time subscriber alerts.
haadi@portfolio:~$ mpv --no-audio --loop demo.mp4
haadi@portfolio:~$ cat project.yml
- technologies
- SignalR, Isolation Forest (ML), Azure App Service, Google OAuth, Email alerts
- role
- Frontend, backend and database; a teammate built the ML model
- year
- 2026
- status
- Complete
How it wasbuilt
haadi@portfolio:~$ cat -n the-problem.txt
- There's no single, live place to see which Pakistani cities and sectors are being targeted, by what kind of attack, right now, incident information is scattered and unverified.
haadi@portfolio:~$ cat -n the-approach.txt
- Crowdsource the intelligence, but never publish it raw. Reports flow through machine-learning triage and human moderation before they reach the map, the analytics and anyone's inbox.
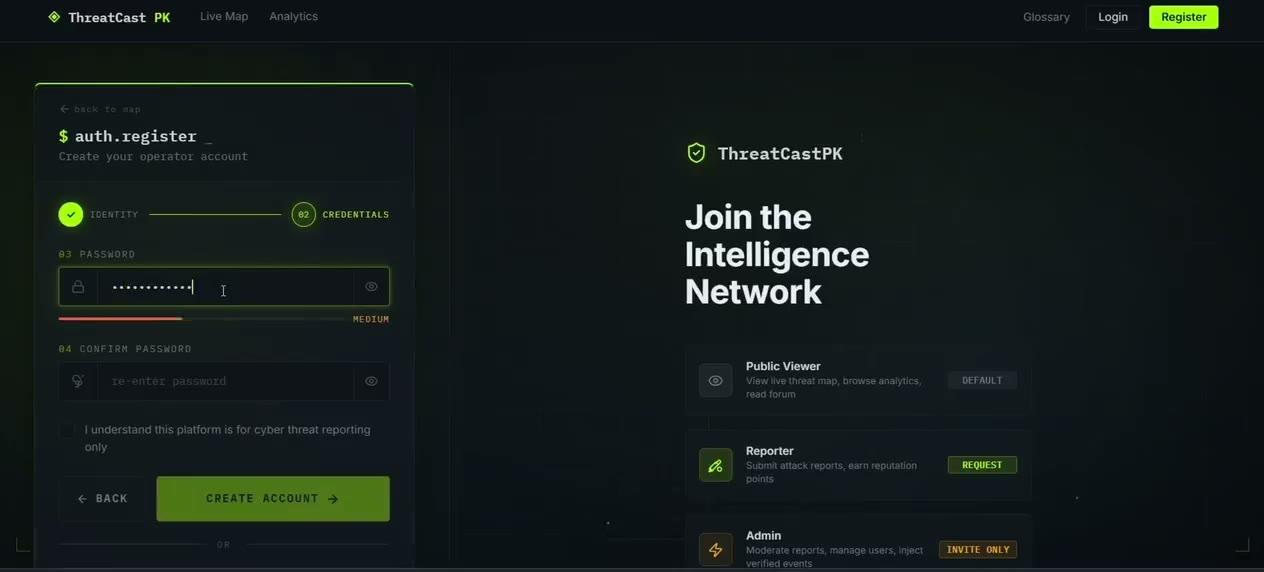
- Public viewer (default): live threat map, analytics and forum.
- Reporter (by request): submit attack reports and earn reputation points.
- Admin (invite only): moderate reports, manage users and inject verified events.
haadi@portfolio:~$ cat -n implementation.txt
- A live threat map of Pakistan with 1H, 6H, 24H and 7D windows, colour-coded by attack type (DDoS, ransomware, phishing, malware), alongside a live feed and a sector-risk panel for banking, telecom, healthcare, education, government and energy.
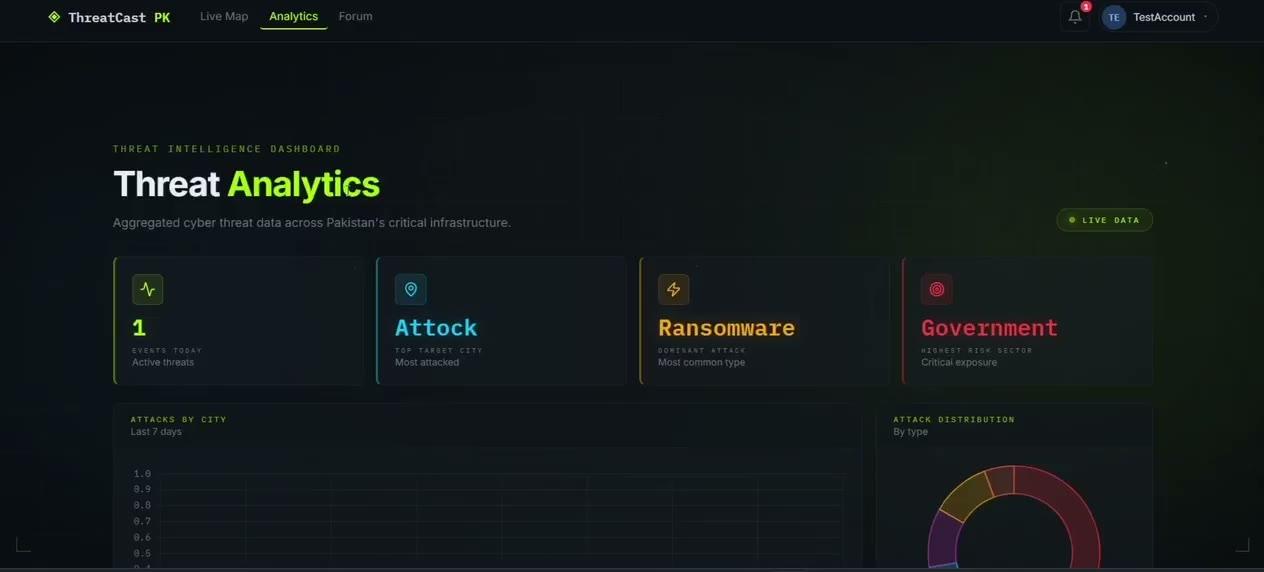
- The analytics dashboard aggregates events today, the most-attacked city, the dominant attack type and the highest-risk sector, with attacks by city over seven days and a distribution by type.
- Attack reports: type, target sector, city and a 1 to 5 severity scale
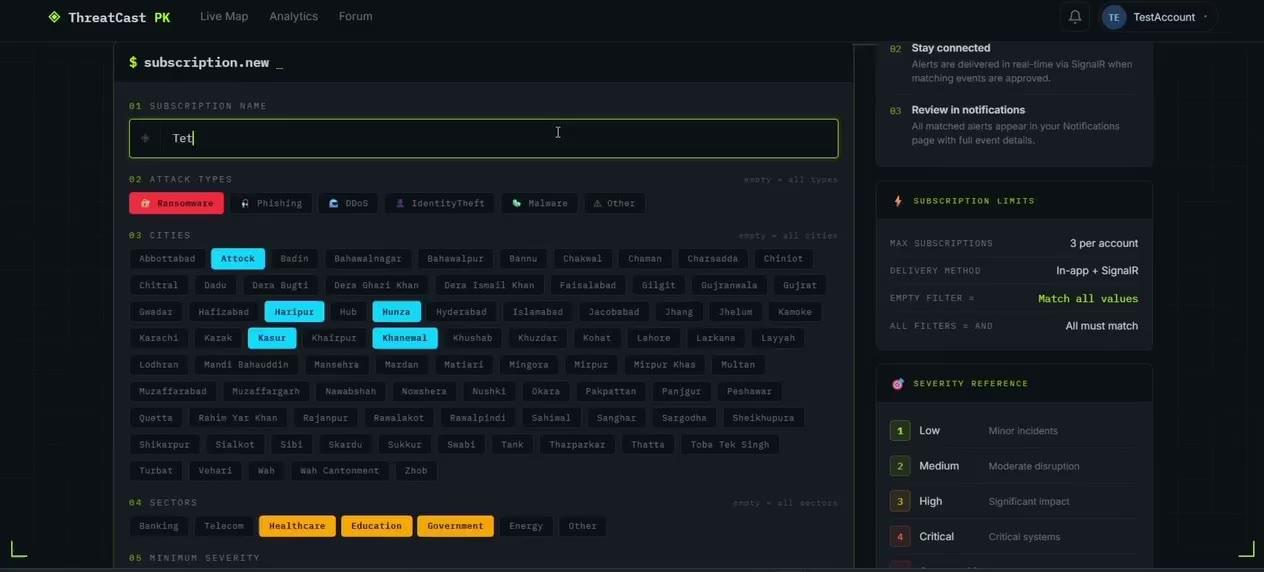
- Alert subscriptions: attack types, cities, sectors and minimum severity, up to 3 per account, empty filter matches all, filters combine with AND
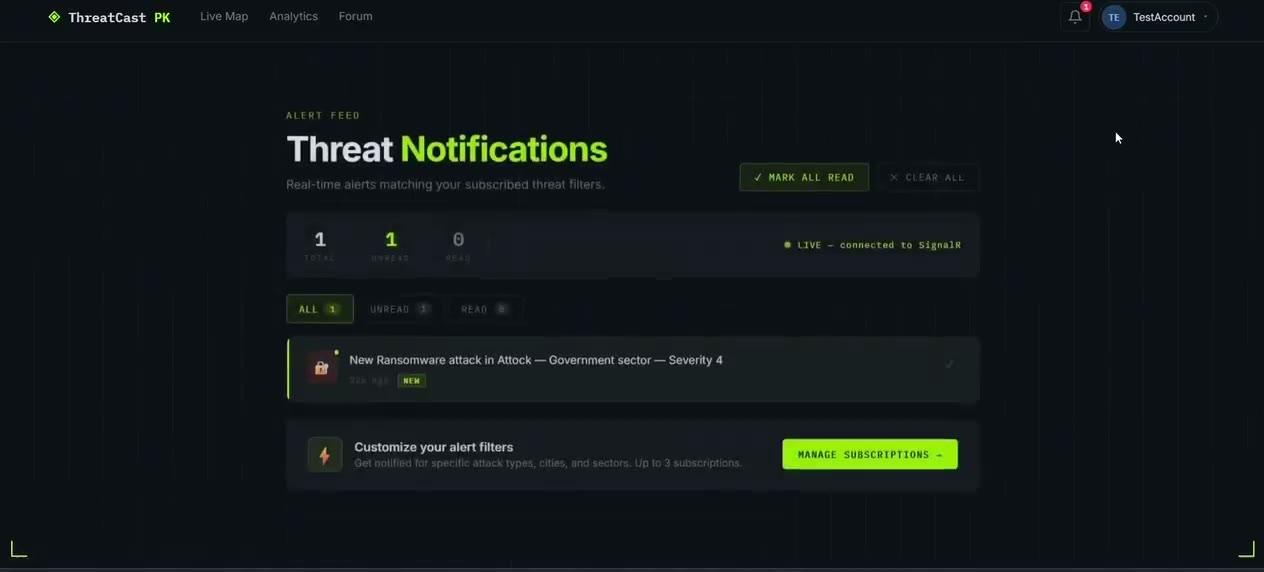
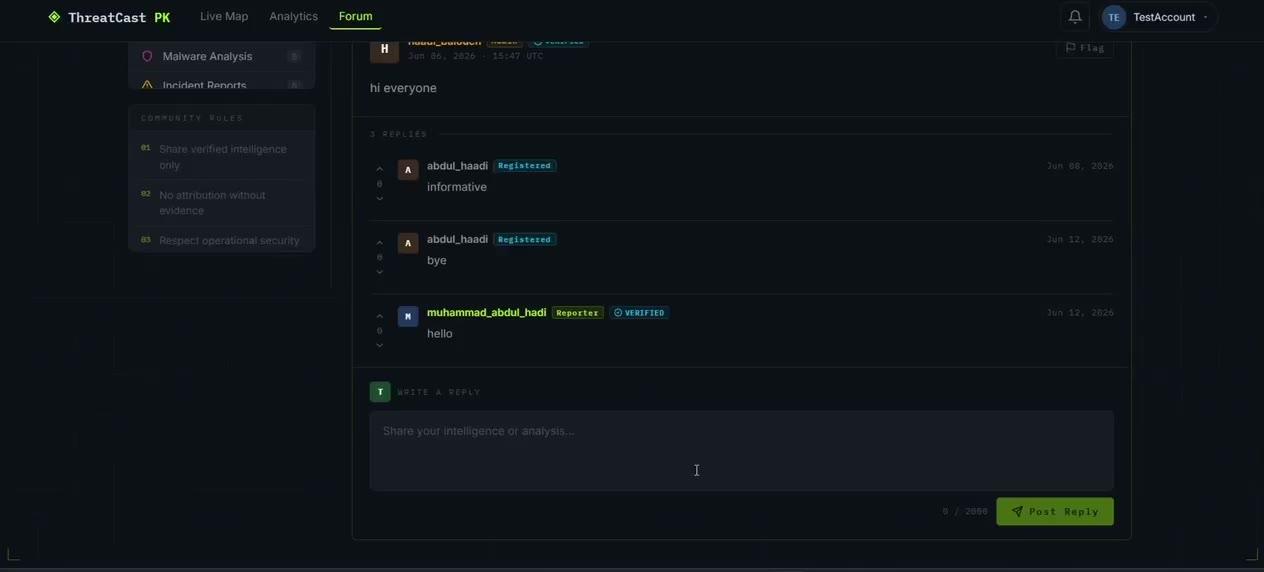
- Delivery in-app over SignalR and by email, plus a threat forum with community rules
What itproved
haadi@portfolio:~$ cat -n security-details.txt
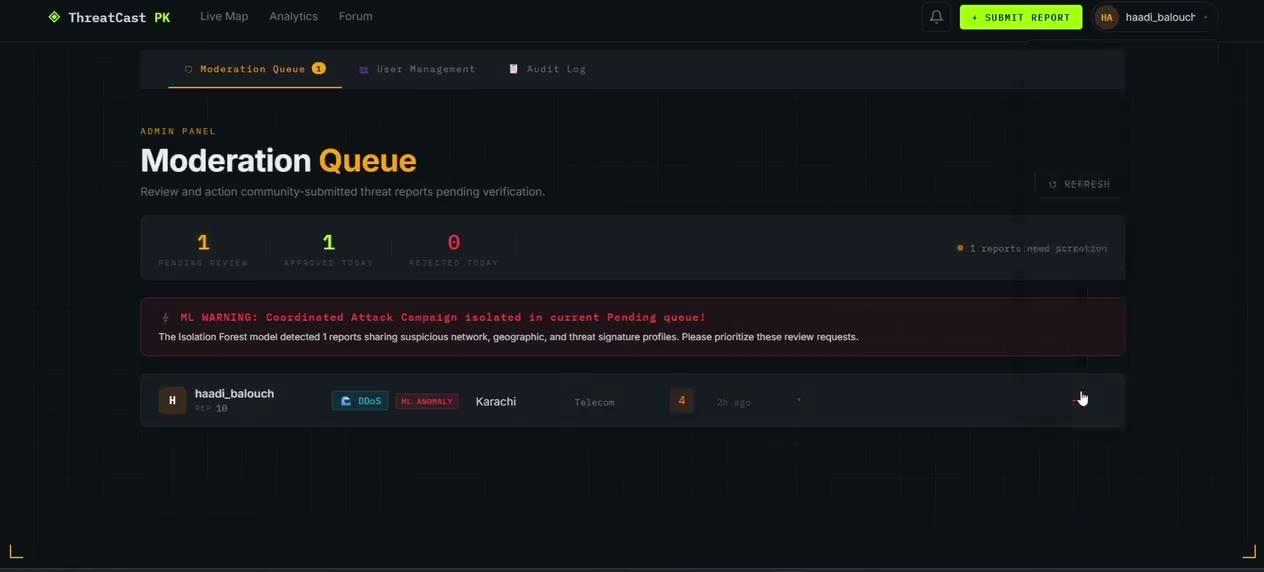
- Every submission lands in a moderation queue. An Isolation Forest model scores pending reports and raises an ML warning when several share suspicious network, geographic and threat-signature profiles, a likely coordinated campaign, so moderators review those first.
- Accounts are protected with email verification, new-login email alerts, Google sign-in, a password-strength meter and 'sign out of all sessions'; admins get user management and an audit log.
haadi@portfolio:~$ cat -n result.txt
- Access roles, admin invite-only
- 3
- Access roles, admin invite-only
- Anomaly triage before publishing
- ML
- Anomaly triage before publishing
- Map, analytics & SignalR alerts
- Live
- Map, analytics & SignalR alerts
Evidence fromthe lab
haadi@portfolio:~$ eog analytics.jpg
haadi@portfolio:~$ eog moderation-ml.jpg
haadi@portfolio:~$ eog subscriptions.jpg
haadi@portfolio:~$ eog notifications.jpg
haadi@portfolio:~$ eog register-roles.jpg
haadi@portfolio:~$ eog forum.jpg
Stack &links
haadi@portfolio:~$ cat -n technologies-used.txt
signalrisolation forest (ml)azure app servicegoogle oauthemail alerts
Next project